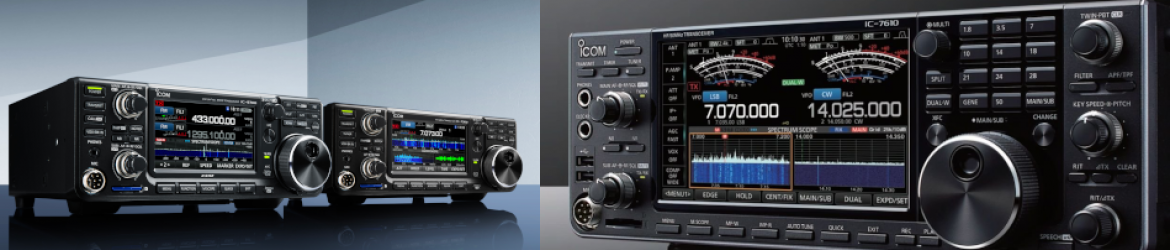
The amateur radio community is witnessing an interesting development. Firmware for some modern Icom transceivers has been decoded, and, for supported models, modified and rebuilt, opening possibilities that were previously beyond the reach of most radio amateurs. At the same time, artificial intelligence is transforming how engineers approach complex reverse-engineering projects.
For decades, amateur radio has been built around experimentation. We modify equipment, develop software, construct interfaces and push the boundaries of what our radios can do.
But modern transceivers are no longer simply collections of RF circuits and analogue controls. They are sophisticated embedded computing platforms, often running proprietary software that determines much of their functionality.
Until recently, investigating that software required considerable specialist knowledge, expensive tools and potentially months of painstaking analysis.
That landscape is beginning to change.
SQ6EMM’s breakthrough: Custom firmware for Icom radios
Polish radio amateur Dawid, SQ6EMM, has published a remarkable project involving the firmware of the Icom IC-705, IC-9700 and IC-905.
His work demonstrates that the firmware update containers used by these radios can be decoded and their internal structure investigated.
More importantly, in the case of the IC-705 and IC-9700, the firmware can be modified, rebuilt and packaged into an update file accepted by the radio’s normal firmware update mechanism.
This is considerably more significant than changing a few configuration parameters or sending undocumented CI-V commands.
It involves understanding the underlying firmware format, extracting executable code, analysing its operation and introducing modifications into the software running on the transceiver itself.
The project is publicly documented on GitHub, together with utilities for decoding, rebuilding and patching supported firmware images.
Project: https://github.com/sq6emm/icom-custom-firmware
What new features are possible?
The custom firmware project introduces functionality particularly relevant to operators using transverters and microwave equipment.
Some of the documented enhancements include:
- Support for up to eight transverter configurations.
- RF frequency displays extending to 122 GHz.
- CI-V frequency translation for external software.
- Configurable maximum transmission power for individual transverters.
- TX delay and PTT inhibit controls.
- Additional spectrum scope settings.
- A/B firmware booting, allowing an alternative firmware image to be retained.
The IC-705 modifications also include extended transmission frequency ranges, although the hardware’s capabilities and applicable licensing restrictions remain important considerations.
For microwave enthusiasts, especially those using transverters with the IC-9700, these are potentially valuable improvements.
They demonstrate how additional functionality can be introduced without changing the underlying RF hardware.
How was the firmware reverse engineered?
One of the most interesting aspects of the project is the documentation describing the Icom firmware update format.
The firmware containers contain several software components, including executable images for the main processor and other subsystems.
The research identified two important transformations used to encode the firmware:
1. An autokey byte transformation
A reversible operation obscures the firmware data using relationships between consecutive bytes and their positions within the image.
2. LZSS compression
The firmware also uses a variant of the LZSS compression algorithm, which must be reversed to recover the original executable image.
Once these operations are understood, the firmware can be extracted into a form suitable for conventional reverse-engineering tools.
The recovered main processor images contain ARM executable code that can be investigated using tools such as Ghidra.
The repository includes scripts and documentation covering the firmware layout, decoding process and reconstruction of update files.
Why the IC-905 is different
An important distinction emerged during the investigation.
The IC-705 and IC-9700 firmware update formats use unkeyed MD5 integrity checks, allowing modified firmware images to be rebuilt with valid checksums.
The IC-905 update format includes RSA-2048 digital signatures; the published research describes signature verification by the radio as a remaining question.
This means that although the IC-905 firmware can be decoded and analysed, rebuilding a modified update with a valid manufacturer signature is a different challenge.
A valid manufacturer signature cannot be recreated without the private signing key. Whether and where a particular device enforces signature verification must be established separately; decoding alone does not answer that question.
This illustrates the difference between a checksum designed to detect accidental corruption and a cryptographic signature intended to authenticate software.
Where does artificial intelligence fit into all this?
This is perhaps the part that interests me most.
Modern AI-assisted development tools are changing how engineers approach complex software problems.
Reverse engineering has traditionally involved manually analysing disassembled instructions, following function calls, identifying memory structures and gradually reconstructing undocumented behaviour.
Tools such as Ghidra have made this work possible for many years.
AI introduces another layer of assistance.
A capable coding assistant can help interpret decompiled functions, suggest relationships between unfamiliar code sections, generate analysis scripts and assist with repetitive investigation.
It can also help developers understand processor architectures, binary formats and unfamiliar software structures.
For example, an engineer might use Ghidra to extract a function from an ARM firmware image, then ask an AI assistant to explain its likely purpose, identify relevant memory operations or suggest how to investigate the surrounding code.
The results still require careful verification.
AI can misunderstand assembly instructions, invent relationships or propose changes that would be unsafe on real hardware.
Nevertheless, it can significantly accelerate the investigative process.
An important distinction: SQ6EMM’s published repositories establish the technical reverse-engineering achievements, but they do not independently establish which AI tools, if any, were used to produce those results.
The broader significance is that projects of this complexity are becoming increasingly approachable when conventional engineering tools are combined with AI-assisted analysis.
Our own experiments at 9H1LO: Exploring firmware emulation
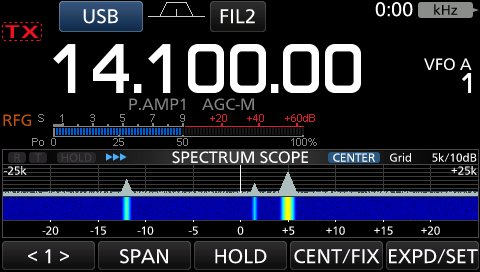
At 9H1LO, we have also been experimenting with Icom firmware investigation and emulation. Our work uses the open-source IC-7300 homebrew project by Jarkko Vääräniemi, a separate project from SQ6EMM’s IC-705 and IC-9700 modifications.
Our interest is not simply in modifying a radio to unlock additional features.
We want to understand how these embedded systems operate, how their firmware interacts with hardware and whether portions of that behaviour can be studied in a controlled virtual environment.
Our experiments run the project’s IC-7300 emulator in an Ubuntu virtual machine. We verified its reference display and MENU control, and explored a virtual SD card and homebrew app loader. These are emulator experiments; we have not validated the loader on a physical radio.
The idea is to create a development environment in which firmware components can be investigated without exposing an expensive transceiver to unnecessary risk.
Why use an emulator?
Modern Icom transceivers incorporate specialised embedded processors, memory devices, DSP components and interfaces to RF hardware.
Running firmware designed for these systems on a conventional computer is not as straightforward as executing a normal application.
An emulator must reproduce enough of the original processor and hardware environment for the firmware to execute meaningfully.
Depending on the level of emulation, this may involve processor instruction emulation, memory mapping, interrupt handling and simulated peripherals.
Not every hardware function needs to be reproduced immediately.
Even limited execution and debugging capabilities can provide useful insights into the firmware’s internal behaviour.
Combining emulation with AI-assisted development
Our experimentation also explores the use of AI coding tools to assist with the development and investigation process.
AI can help examine firmware structures, explain unfamiliar routines and develop the scripts and supporting software needed for experimentation.
However, the real challenge remains ensuring that the results correspond to the actual behaviour of the embedded system.
An AI-generated explanation is not proof that a particular function behaves as described.
Similarly, successfully loading firmware into an emulator does not necessarily mean that the firmware is executing correctly or that the complete transceiver has been emulated.
At this stage, our work remains experimental.
We are not claiming to have developed a fully operational virtual Icom transceiver.
The objective is to build an understanding of the firmware and investigate what may eventually become possible through emulation, debugging and controlled experimentation.
As the investigation progresses, we intend to share further technical findings and practical experiences on 9H1LO.
A particularly interesting development: The A/B bootloader
Another significant aspect of SQ6EMM’s work is the custom A/B firmware bootloader.
The concept allows an alternative firmware image to be retained on the radio, giving operators a means of switching between firmware slots.
For experimental development, this is an important capability.
However, it should not be confused with a completely risk-free recovery mechanism.
Installing the modified bootloader requires rewriting a critical part of the radio’s firmware.
An interruption during this process could leave the equipment unable to boot normally, potentially requiring direct access to the flash memory using external programming equipment.
The project’s documentation specifically warns users about this risk.
Anyone considering installing modified firmware should understand the implications and ensure that suitable recovery arrangements are available.
The browser-based firmware patcher
Rather than distributing complete modified Icom firmware images, SQ6EMM provides a web-based patching utility.
Users download the official firmware from Icom and supply it to the patcher.
The patching operation takes place locally within the browser.
The tool checks the supplied firmware against supported versions and applies the available modifications.
This is an interesting approach because it avoids redistributing complete proprietary firmware images.
It also provides a more accessible interface for technically capable users who may not want to execute the individual decoding and rebuilding tools manually.
The patcher is available at:
https://sq6emm.github.io/icom-custom-firmware/
Of course, users should understand the risks before installing any unofficial firmware.
What does this mean for Icom and other manufacturers?
Modern amateur radio equipment is increasingly defined by software.
The hardware may remain capable of operating for many years, but the functionality available to the operator is often determined by the manufacturer’s firmware development priorities.
Once a product reaches the end of its commercial development cycle, additional features may never arrive, even when the underlying hardware could potentially support them.
Community-driven firmware research introduces another possibility.
It raises questions about the extent to which owners should be able to inspect, understand and modify the software running on equipment they have purchased.
Manufacturers have legitimate concerns about safety, regulatory compliance, intellectual property and product reliability.
At the same time, amateur radio has always encouraged technical experimentation and innovation.
Finding a reasonable balance between these interests will become increasingly important.
Is this the beginning of community-developed amateur radio firmware?
It is still too early to say.
Reverse engineering a firmware format is one achievement. Maintaining reliable alternative firmware for a complex commercial transceiver is another challenge entirely.
There are many practical difficulties, including undocumented hardware, compatibility between firmware versions, RF safety, testing and long-term maintenance.
Nevertheless, the work demonstrated so far is impressive.
It shows that modern amateur radio firmware is not necessarily beyond the reach of independent researchers.
And with AI-assisted development tools becoming increasingly capable, the number of people able to contribute to these investigations may continue to grow.
Final thoughts from 9H1LO
For me, this development represents something fundamental about amateur radio.
Our hobby has never been solely about purchasing equipment and using it exactly as supplied.
It has always been about understanding technology, experimenting with new ideas and finding ways to improve what already exists.
The work carried out by SQ6EMM is an excellent example of that spirit.
The combination of firmware reverse engineering, emulation and AI-assisted development opens some fascinating possibilities for future experimentation.
Our own work at 9H1LO is still in its early stages, but it is an area I intend to continue exploring.
Whether these developments eventually lead to more community-developed firmware, improved interoperability or simply a better understanding of the equipment we use, they are certainly worth following.
73 de 9H1LO
References and further reading
SQ6EMM: Icom Custom Firmware
https://github.com/sq6emm/icom-custom-firmware
SQ6EMM: Firmware Reverse Engineering Tools
https://github.com/sq6emm/ic705-ic9700-ic905-bring-your-own-firmware
Web-Based Firmware Patcher
https://sq6emm.github.io/icom-custom-firmware/
Community Discussion
https://mikrofale.cafe/showthread.php?tid=1296
Official Icom Website
Disclaimer: This article is intended for technical discussion and educational purposes. Firmware modifications can cause equipment failure, affect regulatory compliance and potentially void warranties. The projects discussed are independent of Icom and are not officially endorsed by the manufacturer. The 9H1LO emulator experiments described here are preliminary research, not a claim of completed firmware emulation.